Step 01Layer 05 · Regulators and partner banks
Review
We map the AML and financial crime regulations that apply in each country you operate in, and gap-assess your current set-up.
Tuned to regulatory standards. Run by experts.
We are the team who make your compliance technology work. Our FinCrime specialists run it every day: alerts, KYB files and escalations to the MLRO, every decision documented.
Noise in
Decisions out: Documented, defensible decisions.
Grow with confidence.Fintech · Payments · Crypto · Anywhere in the world
01 / The human layer
We are not an AI vendor. We build your financial crime compliance framework around the rules in every jurisdiction you serve, then make your technology run to that standard, every day.
We map the AML and financial crime regulations that apply in each country you operate in, and gap-assess your current set-up.
We update your AML policies and business-wide risk assessment so they meet every regulatory obligation.
Policy becomes clear procedures, decision trees and checklists that any new team member can follow from day one.
Monitoring, screening and AI calibrated to your framework, regulatory standards and global best practice.
Your tuned systems raise the alerts that matter.
Our specialists check every alert and KYB file against the customer and the context.
A documented closure, or an escalation to the MLRO with the evidence in place.
Monthly reporting and an evidence pack for regulators, auditors and partner banks.
Transactions, customer onboarding and screening data from your platform.
Your rules and models, calibrated by us to regulatory standards and global best practice, flag unusual activity at machine speed.
First-line analysts investigate every alert and KYB file, document the rationale and make the call.
Policies, risk assessment and procedures owned here. Escalations decided and filed; monitoring tuned, stress-tested and documented.
A clear, evidenced story regulators, auditors and partner banks can follow in any jurisdiction, from alert to outcome.
02 / Capabilities
Alert reviews, KYC and KYB at scale: every business traced to its ultimate beneficial owners, screened and risk-rated. Specialists on your backlog within 72 hours.
Independent tuning and stress testing of your monitoring and AI, with SOPs and an evidence pack.
Your AML policies, procedures and controls tested by independent specialists, with a board-ready report.
Regulatory Hospitality: entity, local directors, MLRO, compliance team and regulator liaison for your CASP licence.
Official ICA partner: ICA certifications with partner discount codes, plus bespoke training for compliance teams and boards.
03 / Know who you serve
04 / Proof
Since 1 July 2026, only MiCAR-authorised crypto-asset service providers may serve clients in the EU.
Regulatory Hospitality arranges the directors, MLRO, operations and dossier your application needs.
05 / People
Our leadership has been the MLRO, filed the reports and answered to the regulator. Every engagement is led by a named partner, and every deliverable is quality-assured independently before it reaches you.
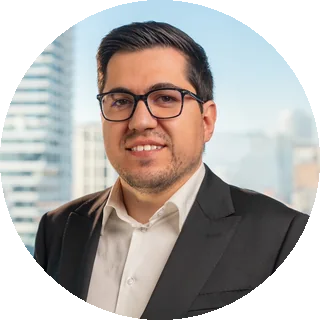
Managing Partner
Master of Laws (LLM) · CAMS
Over ten years in financial crime compliance across crypto, payments and Big 4 consulting. Embedded MLRO of an AUSTRAC-regulated virtual asset service provider and former Head of Compliance and MLRO of a UK crypto payments processor. Leads our MiCAR authorisation work before Bulgaria’s Financial Supervision Commission.
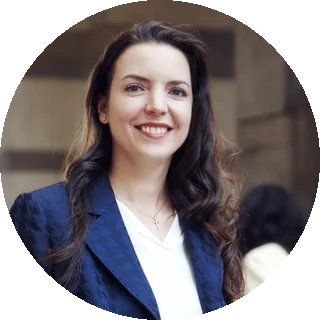
Principal, AML/CFT and Sanctions
ICA International Diploma in AML · Former FCA-approved MLRO (SMF17)
Over twelve years in financial crime compliance and four Head of Compliance and MLRO appointments, including MLRO of an EU e-money institution with direct FIU reporting, and Head of Compliance and MLRO of a crypto-asset exchange and custody platform.
Senior Compliance Analyst
Fifteen years in payments, fintech and crypto compliance. Former Head of Compliance and MLRO of an FCA-registered e-money agent serving crypto-asset businesses; built a compliance training academy for more than 200 staff; led AML investigations and SAR reporting at a global payments group.
Crypto Regulation and Travel Rule · Transaction Monitoring certifications
Senior Compliance Analyst
Seven years in KYB, KYC and financial crime prevention. Drafted SARs to the UK National Crime Agency at a Tier 1 UK e-money institution, co-designed the first KYC quality assurance framework at a Tier 1 global crypto exchange, and led KYB for high-risk acquiring at a leading EU payments institution.
CAMP · CFCP
Compliance Analyst
Risk-based KYC reviews at a Tier 1 UK bank, alert review at a Tier 1 US bank and financial crime investigations at a Tier 1 global crypto exchange, with audit-ready case documentation in high-volume teams.
LexisNexis · Chainalysis
Regulator experience: FCA (UK) · AUSTRAC (Australia) · FSC (Bulgaria) · DNB (Netherlands) · FINTRAC (Canada) · VARA (UAE) · FIU reporting in the UK and Bulgaria
Jurisdictions covered: EU, UK, Australia and the UAE. Former employers and clients are not named, to protect confidentiality. More senior analysts join as engagements scale, under the same quality assurance framework.
06 / Contact
A licence to secure, a backlog to clear, KYB to scale or a team to train. Tell us where you are and we will come back with a clear next step.
FAQ
At a glance
AskRegulations is a financial crime compliance consultancy for fintech, payments, crypto and regulated gaming firms. We run outsourced AML operations, perform independent AML audits, support crypto firms through MiCAR authorisation and train compliance professionals as an official ICA partner, with bespoke programmes for teams and boards, from the EU and the UAE for clients worldwide.
AskRegulations is a financial crime (FinCrime) compliance consultancy. We provide the human layer behind your monitoring tools and AI: our specialists work your alerts and KYC and KYB files, we secure MiCAR authorisation for crypto-asset service providers, and we train compliance teams through ICA-accredited programmes.
No. We are a human vendor. We calibrate your monitoring, screening and AI to regulatory standards and global best practice, then our FinCrime specialists run it: they investigate the alerts, make and document the decisions, and escalate suspicious activity to the MLRO.
Yes. KYB is one of our core capabilities. We verify businesses against registries and documents, trace ownership to the ultimate beneficial owners, screen directors and owners for sanctions, PEPs and adverse media, evidence source of funds and wealth, and risk-rate each business. We handle onboarding, periodic reviews and remediation backlogs at scale.
Financial crime compliance consulting helps regulated firms prevent money laundering, terrorist financing, sanctions breaches and fraud, and prove to regulators that their controls work. It covers policies and risk assessments, customer and business due diligence, monitoring, investigations, independent testing and training.
Fintechs, payment and e-money institutions, crypto exchanges, custodians and brokers, and regulated gaming operators worldwide, from firms preparing their first licence application to established institutions handling high alert volumes.
AskRegulations operates through two companies under common ownership: AskRegulations Ltd in Sofia, Bulgaria (EU), and AskRegulations Gulf – FZCO in Dubai Silicon Oasis, Dubai (UAE). We work with clients globally.
Within 72 hours. Once we agree the scope, our FinCrime specialists are deployed on your backlog, working inside your systems and under your own policies.
Yes. We work with fintech, payments and crypto firms worldwide. Every engagement starts with a review of the AML and financial crime regulations that apply in each jurisdiction you operate in, from MiCAR and EU AML rules to your local requirements, and we build your framework around them.
Yes. Tell us your jurisdiction and we will confirm the local requirements before we start. Our specialists test your AML policies, procedures and controls as an independent external expert and report to your board. We never audit work we designed or run.
Yes. We adapt your AML policies and business-wide risk assessment to your regulatory obligations, then turn them into clear procedures, decision trees and checklists that any new team member can follow from day one.